
MetaFend Platform.
Holistic offensive assessment, expert validation, and executive clarity in one place.
Chained weakness. Connected environments.
Multiple entry points. Shared pivots. Business impact
Entry points
Toll boundary bypass
Application weakness
Exposed deployment secret
Identity & Cloud
Excessive permissions
Run command access
Broad data access
Internal network
Remote command execution
Excessive AD rights
Delegation misconfiguration
Business impact
Data exposure
Operational impact
Privilege access
Highlighted chain
AI agent - AWS role - AWS systems manager - Domain-joined host - Service identity - RBCD - Domain control
Alternative routes
Additional paths from other entry points and through resources
Illustrative scenario - Paths depend on permissions, reachability and validated weaknesses.
All attack paths revealed.
AI systems, external exposure, internal networks, applications including static code analysis, cloud and people. All emulated as one connected surface, because that is how an attacker sees it. Not a scanner with a report template: threat emulation that chains weaknesses into complete attack paths.
Agent-to-domain compromise
AI Agent
Entry pointAWS SSM
Cloud pivotActive directory
Impact1. AI Agent
Agent compromiseTool execution context
2. Identity
AWS role accessOver-permissive identity
3. Cloud resources
AWS systems managerRun command allowed
4. Technique
RBCD abuseDelegation rights misconfigured
5. Asset
Internal hostDomain-joined managed node
6. Critical impact
Domain compromisePrivilege domain access
Path conditions
Requires an SSM-managed host and sufficient AD delegation rights, domain impact depends on the target reached
Ranked by your business, not by a generic score.
Findings are prioritized by what they actually reach in your environment.
Asset criticality, exposure, and exploitability. The platform tracks how long critical findings stay open, who owns them, and whether risk is going down.

Business risk register
Open risks
high priority
Overdue reviews
Domain compromise
criticalBusiness impact: loss of control over core systems.
Core infrastructure
Cross-environment path
Review evidence

Mitigate
Infrastructure
In progress
12 days

Restrict cloud execution rights and correct AD delegation
AI Platform - Assigned
Infrastructure - Awaiting retest
Where the chain gets complex, our operators take over.
Automation covers breadth at machine speed. Our offensive team is there for the part automation cannot do on its own: tying separate weaknesses into the long, improbable attack chains a real adversary would build — across surfaces, across systems — and pushing each one to where it actually ends. That is the difference between a list of issues and proof of how far an attacker gets.
Capabilities.
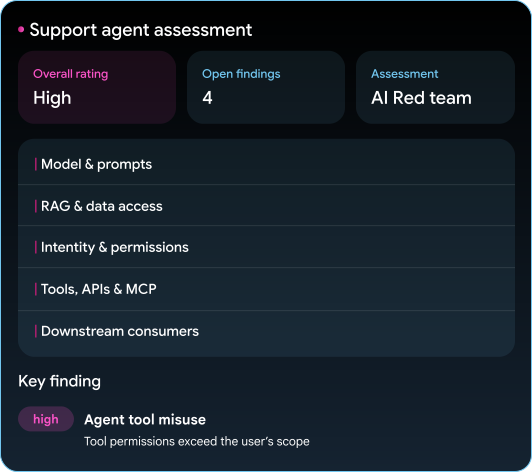
Your AI isn't a model. It's a system — connected to your data, running under your identity, acting on your infrastructure. We test it the way attackers will.
- Model-layer attacks (entry point)
- Data reach (RAG, vector stores, poisoning)
- Identity & permission envelope
- Tool/API surface (agents, MCP, chaining)
- Downstream consumers & monitoring gaps
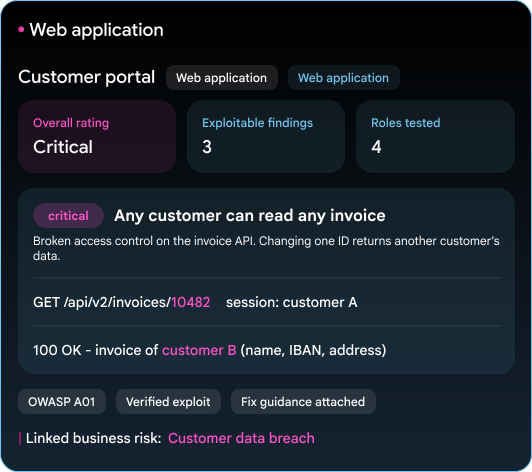
Assess web applications and APIs for security weaknesses through scoped, authenticated and unauthenticated testing. Findings are prioritized by business impact and paired with clear remediation guidance.
- Authentication and session management
- Authorization and access control
- Input handling and API security
- Business logic and configuration
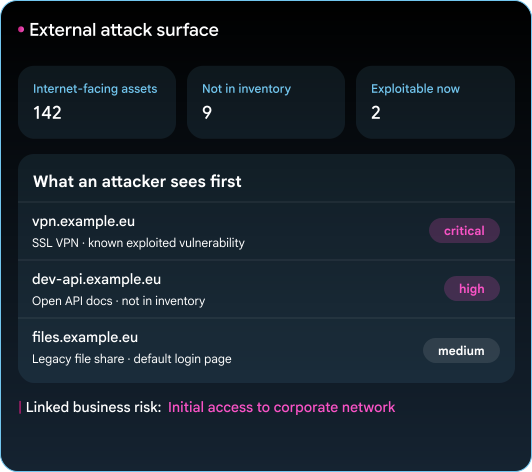
Map internet-facing assets and review exposed services, domains, and configurations to identify risks before they can be exploited.
- Asset and subdomain discovery
- Exposed service review
- DNS, TLS, and security headers
- Risk prioritization and validation
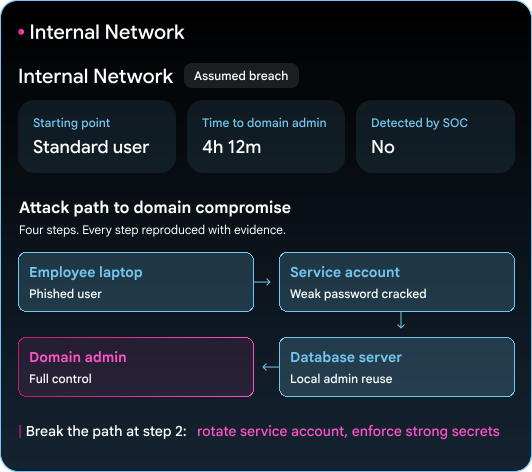
Assess internal environments from an assumed-breach perspective to identify weaknesses that could lead to unauthorized access or lateral movement.
- Network segmentation and trust boundaries
- Identity and privilege exposure
- Service and configuration review
- Lateral movement risk assessment
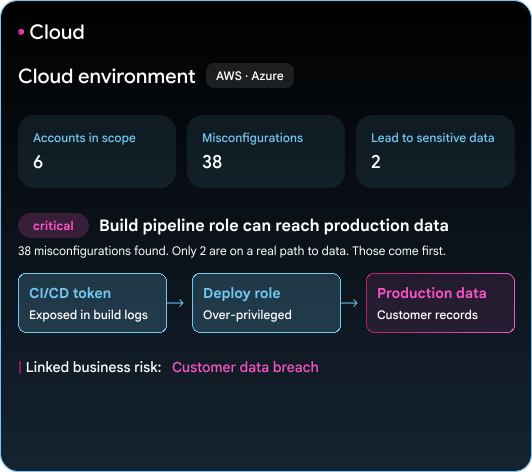
Review cloud accounts and workloads for identity, configuration, and exposure risks, with practical recommendations prioritized for remediation.
- IAM permissions and role review
- Storage and network exposure
- Logging, monitoring, and key management
- Workload and policy configuration
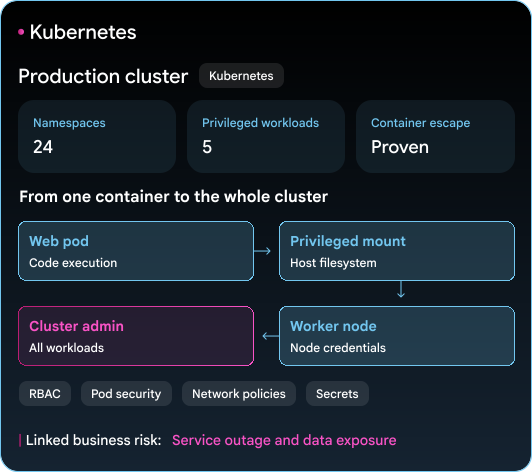
Evaluate Kubernetes clusters and workloads for gaps in access controls, configuration, and isolation, then provide actionable hardening guidance.
- RBAC and service-account permissions
- Cluster and API server configuration
- Workload security and secrets
- Network policies and namespace isolation
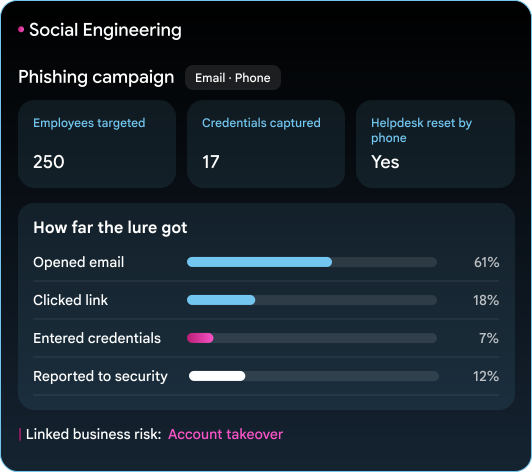
Measure organizational resilience through approved, controlled social-engineering simulations, then identify opportunities to improve awareness and response processes.
- Phishing and messaging simulations
- Pretext and impersonation scenarios
- Reporting and response effectiveness
- Awareness trends and improvement actions
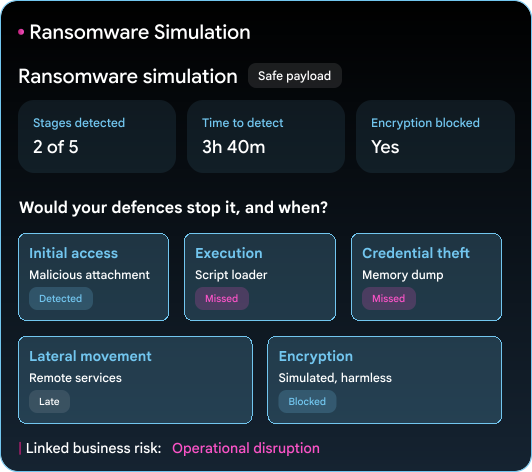
From one workstation treated as compromised, the platform opens an outbound connection to external infrastructure, mass-encrypts dummy data on a file share you designate and can copy it out. It measures whether your defenses detect and stop this attack, and how fast.
- Assumed-compromise workstation start
- Outbound connection detection
- Mass-encryption detection and response time
- Optional exfiltration of dummy data
ROI
-
Holistic Cyber Threat Exposure Management and Compliance Framework Governance in One Platform
-
Reduce the vulnerabilities and misconfigurations that actually need to be fixed by your IT from thousands to a handful.
-
Multiple assessment capabilities in one platform, from AI systems to cloud, networks, application with static code review and people.
-
Previously unknown critical and high-severity attack paths to organization crown jewels, found and validated in a single assessment.
How we do it.
-
Define the threat emulation scenario
Different starting points, different crown jewels, unique business-impact objectives, tailored audit test scenarios.
-
Reconnaissance
Map what you actually expose, from the outside in.
-
Emulation
Run real adversary techniques against the agreed scope.
-
Chaining
Our operators connect what automation surfaced into complete attack paths.
-
Prioritization
Rank findings by business impact and reachability.
-
Re-test
Re-validation as your environment changes.
AI-native by architecture
MetaFend was built around AI from the first line of code: AI drives the emulation, and AI systems are a first-class target of it. This is not an AI feature added to a legacy scanner. It is the same core engine our research team uses to identify real-world zero-day vulnerabilities in cloud-AI and LLM-orchestration infrastructure. What it finds in the wild is what it brings to your environment.
-
Scope & threat model
We define the deployment boundaries, integration map, and adversary goals with your architecture and security leads. No generic questionnaires an actual working session.
-
Adversary simulation
Our engineers execute real techniques, including indirect injection, privilege chaining, exfiltration, against a staging or production-equivalent environment agreed in scope.
-
Finding & framework mapping
Attack paths are documented with reproducible evidence, mapped to international standards, and risk-scored for engineering triage.
Stay ahead of whatever comes next.
See what an attacker would find before one does.
BOOK A DEMO